
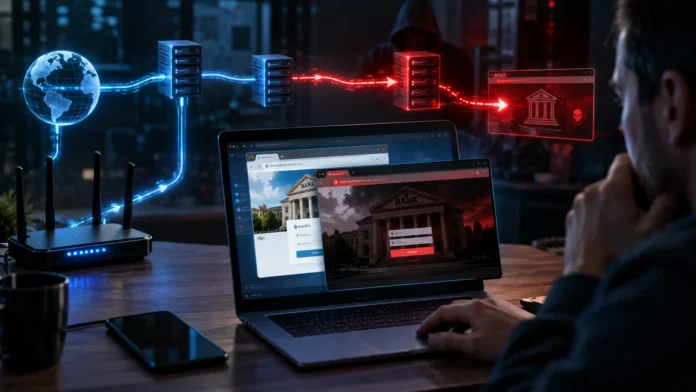

Pharming is a cyber security attack that secretly redirects users from legitimate websites to fraudulent ones designed to steal sensitive information. Unlike many scams that require a person to click an obviously suspicious link, pharming can send victims to a fake website even when they enter the correct web address. This makes the attack especially deceptive and potentially difficult to notice.
Cybercriminals may use pharming to collect usernames, passwords, banking details, payment information, or other confidential data. Fake websites are often designed to closely resemble trusted banking portals, email services, online stores, or business platforms. A user may therefore enter sensitive information believing they are communicating with the genuine organization.
Understanding what pharming is in cyber security can help individuals and businesses recognize unusual website behavior and strengthen their defenses. This guide explains how pharming works, common attack methods, the difference between pharming and phishing, warning signs, prevention strategies, and what to do if you suspect you have been targeted.
What Is Pharming in Cyber Security?
Pharming is a cyberattack that manipulates the process used to connect users with websites. Instead of directing a person to the legitimate destination associated with a web address, the attacker causes the browser to load a malicious website. The fake site may look almost identical to the original so victims feel comfortable entering private information.
The name pharming is closely related to phishing because both techniques often aim to steal credentials or financial information. However, pharming usually relies more heavily on technical manipulation than on persuading users to click a fraudulent message. Attackers may alter local computer settings, compromise networking equipment, or interfere with systems responsible for translating domain names.
Because the user may type the correct address manually, traditional awareness advice such as “do not click suspicious links” is not always enough. Pharming demonstrates why cyber security requires both safe user behavior and technical controls. Secure DNS services, updated software, browser protections, network monitoring, and strong authentication can all reduce exposure.
How Does a Pharming Attack Work?
When you enter a website address into a browser, your device needs to identify the server associated with that domain name. The Domain Name System, commonly called DNS, helps translate human-readable addresses into the numerical IP addresses computers use. Pharming attacks attempt to interfere with this process so the wrong destination is returned.
An attacker may manipulate information stored on a victim’s device or target DNS infrastructure used by many users. If the manipulation succeeds, someone attempting to visit a legitimate banking or email website can be silently redirected to an attacker-controlled page. The fake page then attempts to collect whatever information the victim submits.
The danger is that the browser may appear to behave normally from the user’s perspective. The victim types a familiar address, presses Enter, and sees a recognizable website design. Unless they notice problems with the domain, certificate, page behavior, or authentication process, they may have little reason to suspect the destination is fraudulent.
Common Types of Pharming Attacks
One form of pharming involves changing information on an individual computer. Malware or another unauthorized program may alter local settings that influence how domain names are resolved. This can redirect selected websites toward malicious servers without requiring the attacker to compromise a larger internet service.
DNS-based pharming targets infrastructure responsible for resolving website addresses. If attackers compromise or poison DNS information, multiple users may receive incorrect results when attempting to visit legitimate sites. This can potentially make infrastructure-level pharming more widespread than attacks limited to one infected device.
Attackers may also target home or business routers by exploiting weak passwords, outdated firmware, or configuration vulnerabilities. A compromised router can potentially change DNS settings for multiple connected devices. Users may therefore be redirected even when their computers and phones do not contain obvious malicious software.
Pharming vs. Phishing: What Is the Difference?
Phishing generally depends on social engineering. Attackers send deceptive emails, text messages, social media messages, or other communications designed to convince victims to click malicious links or provide sensitive information. The success of the attack usually depends heavily on whether the recipient believes and acts on the message.
Pharming can require much less interaction from the victim. Someone may manually enter a legitimate web address and still reach a fraudulent website because the underlying routing or DNS information has been manipulated. This makes pharming particularly concerning because careful users can potentially encounter the attack without making an obvious mistake.
Both threats can lead to credential theft, financial loss, account compromise, or identity fraud. The defenses also overlap, including strong authentication, browser security, user awareness, updated software, and monitoring. However, pharming additionally highlights the importance of securing DNS infrastructure, routers, endpoint configurations, and other networking components.
What Information Can Pharming Steal?
Login credentials are among the most common targets because stolen usernames and passwords can give attackers access to email, financial accounts, cloud services, or business systems. A fraudulent login page may capture credentials immediately after the victim submits them. Attackers can then attempt to use that information against the real service.
Financial information is another valuable target. Fake online banking or payment pages may request card numbers, security codes, account information, or other details that can support fraud. Because many users expect financial websites to request sensitive information, a professionally designed imitation can appear convincing.
Attackers may also collect personal information such as names, addresses, phone numbers, identification details, or security answers. Even when the stolen data does not provide immediate account access, criminals may combine it with information from other sources. This can support identity theft, targeted phishing, account recovery abuse, or additional cyberattacks later.
Common Warning Signs of Pharming
An unexpected change in a familiar website can be an important warning sign. The page may use unusual branding, contain spelling mistakes, load differently, or request information that the legitimate service normally does not require. Users should be cautious whenever a trusted website suddenly behaves in an unfamiliar way.
Browser security warnings are another important signal. Certificate errors, unusual HTTPS behavior, unexpected domain changes, or warnings that a connection is not private should not be ignored. Although technical problems can occasionally produce legitimate warnings, entering passwords or financial information before confirming the website is genuine can create unnecessary risk.
Unexpected login failures can also deserve attention. A fraudulent site may collect your credentials and then display an error to make you believe you entered the wrong password. If a familiar service suddenly behaves suspiciously, access it through another trusted device or connection and verify the account before repeatedly submitting credentials.
How to Prevent Pharming Attacks
Keeping operating systems, browsers, routers, security tools, and other software updated can reduce the number of vulnerabilities attackers can exploit. Router firmware deserves particular attention because compromised networking equipment can influence multiple connected devices. Default administrator passwords should also be changed to strong, unique credentials.
Using trusted DNS services can provide additional protection against some forms of manipulation. Organizations may also implement DNS security technologies, filtering, monitoring, and validation mechanisms that help detect suspicious responses. These controls are especially important in environments where employees regularly access sensitive business, financial, or customer systems.
Multi-factor authentication adds another layer of defense when passwords are stolen. Even if an attacker captures login credentials through a fraudulent website, they may still be unable to access the account without an additional verification factor. Users should also avoid ignoring browser security warnings or unusual changes in familiar authentication flows.
How Businesses Can Defend Against Pharming
Businesses should begin by securing network infrastructure and maintaining visibility into DNS activity. Security teams can monitor for unusual domain resolution patterns, suspicious configuration changes, and unauthorized DNS servers. Centralized network management can also make it easier to detect when devices suddenly begin using unexpected settings.
Endpoint security is equally important because malware can alter local configurations and redirect users. Organizations should combine antivirus or endpoint detection tools with patch management, access controls, and application security. Restricting unnecessary administrative privileges can reduce the likelihood that malicious software will successfully modify important system settings.
Employee awareness remains valuable even though pharming is more technical than many phishing attacks. Staff should know how to recognize certificate warnings, unusual login behavior, and unexpected website changes. Broader cyber security awareness can also include topics such as OT security, helping teams understand how digital attacks can affect different technology environments.
What to Do If You Suspect a Pharming Attack
If you suspect you have reached a fraudulent website, stop entering information immediately. Do not submit additional passwords, card details, security codes, or personal information. Close the page and access the legitimate service from a trusted device or known-safe network rather than repeatedly returning through the same connection.
If you already submitted login credentials, change the password as quickly as possible using a trusted device. Enable multi-factor authentication if it is available and review recent account activity for unauthorized access. Financial institutions should be contacted promptly when banking or payment information may have been exposed.
Organizations should involve their security or IT teams so the underlying cause can be investigated. The problem may involve endpoint malware, router settings, DNS infrastructure, or another network configuration issue. Simply changing a password may not solve the problem if users continue being redirected to the attacker-controlled destination.
Why Pharming Is Dangerous for Cyber Security
Pharming is dangerous because it can undermine the trust users place in familiar web addresses. People are often taught to manually type important URLs instead of clicking unknown links, but pharming can potentially defeat that habit. The attack targets the technical process connecting users with websites rather than relying entirely on obvious social engineering.
Large-scale pharming can also affect many users at once when shared infrastructure is compromised. A poisoned DNS service or vulnerable network device may redirect multiple systems toward the same fraudulent destination. This increases the potential impact compared with an attack that targets only one person through one malicious message.
The stolen information can create consequences long after the original attack ends. Passwords may be reused against other services, financial details can support fraud, and compromised business credentials may provide access to additional systems. Preventing pharming therefore protects both individual accounts and the wider digital environment connected to them.
Where Pharming Fits Into Cyber Security
Pharming belongs to a broader category of cyber threats focused on manipulating trust and access. Rather than directly breaking into every target account, attackers change how users reach online services and wait for victims to provide valuable information. This makes the attack a combination of technical compromise and credential theft.
Defending against pharming requires several areas of cyber security to work together. Network security protects DNS and routing systems, endpoint security helps prevent malicious configuration changes, identity security limits the usefulness of stolen credentials, and user education helps people recognize suspicious website behavior.
This layered approach is important because no single protection method can stop every variation. Attackers continually change techniques and may combine pharming with malware, phishing, credential theft, or other attacks. Organizations that combine prevention, detection, authentication, and incident response are better prepared to reduce both the likelihood and impact of compromise.
Conclusion
Pharming in cyber security is an attack that redirects users from legitimate websites to fraudulent destinations, often without requiring them to click a suspicious link. Attackers may manipulate local settings, routers, or DNS information to make fake websites appear during otherwise normal browsing activity.
The main goal is often to steal usernames, passwords, financial information, or personal data. Because victims may manually enter the correct website address, pharming can be more difficult to recognize than traditional phishing. Browser warnings, unexpected website changes, unusual login behavior, and certificate problems should therefore be taken seriously.
Protection involves updated software, secure routers, trusted DNS services, strong authentication, endpoint security, monitoring, and user awareness. Businesses should also maintain incident response procedures for suspected DNS or network manipulation. Combining technical safeguards with careful browsing habits offers the strongest defense against pharming attacks.
FAQs
What is pharming in simple terms?
Pharming is a cyberattack that redirects you from a legitimate website to a fake one. The fraudulent site is usually designed to steal passwords, financial details, or other sensitive information.
Is pharming the same as phishing?
No. Phishing usually tricks users into clicking malicious links, while pharming manipulates website routing or DNS information. A pharming victim may reach a fake site even after typing the correct address.
Can antivirus software stop pharming?
Antivirus software can help detect malware that changes local settings, but it cannot prevent every pharming attack. Secure DNS, router protection, updates, browser security, and multi-factor authentication provide additional defense.
How do I know if a website has been pharmed?
Warning signs can include certificate errors, unexpected design changes, strange login behavior, unusual domain names, or requests for information the site normally does not ask for. Always verify suspicious pages before entering credentials.
What should I do after entering information on a fake website?
Change affected passwords immediately from a trusted device, enable multi-factor authentication, and review account activity. Contact your bank if financial information was exposed and report workplace incidents to your IT or security team.




