
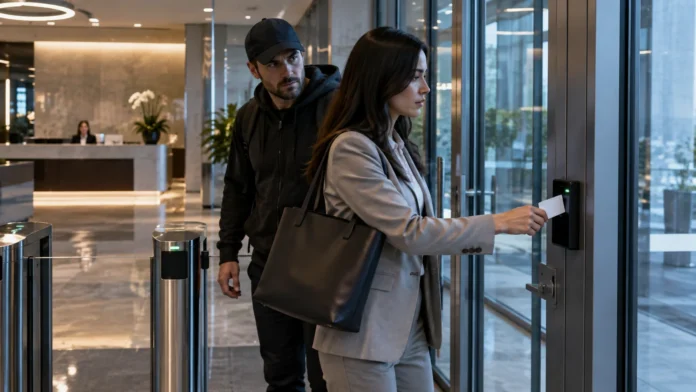

Tailgating in cyber security is a physical social engineering attack where an unauthorized person gains access to a restricted area by following someone who is legitimately allowed to enter. Instead of hacking software or stealing passwords online, the attacker takes advantage of human trust, politeness, distraction, or weak physical access controls to bypass security.
This type of attack can affect offices, data centers, laboratories, server rooms, warehouses, and other restricted locations. Once inside, an intruder may access computers, steal documents, connect malicious devices, observe sensitive information, or enter areas containing critical infrastructure. Understanding how tailgating works can help organizations strengthen both physical and cyber security.
What Is Tailgating in Cyber Security?
Tailgating is an unauthorized physical access technique in which an attacker follows an authorized person through a secured entrance. The legitimate employee may use a badge, key card, biometric scanner, or security code, while the attacker slips through before the door closes. In many cases, the employee does not realize that security has been bypassed.
The attacker may pretend to be another employee, delivery worker, contractor, cleaner, visitor, or technician. They might carry boxes, hold a phone, wear professional-looking clothing, or act as though they belong in the building. These small details help reduce suspicion and encourage employees to hold doors open.
Tailgating is considered a form of social engineering because it targets human behavior rather than exploiting a technical software vulnerability. Attackers rely on courtesy, confidence, urgency, or authority to influence the person in front of them. A secure access system can therefore still fail if employees routinely allow unknown individuals to follow them inside.
How Does a Tailgating Attack Work?
A tailgating attack usually begins with observation. The attacker may watch an office entrance to understand when employees arrive, how access badges are used, and whether security guards check identification. They may also identify busy periods when people are more likely to enter in groups and pay less attention to who follows behind them.
Next, the attacker creates a believable reason to be near the secure entrance. They might pretend their badge is not working, claim they forgot it, or carry something that makes opening the door difficult. A helpful employee may then allow them to enter without following the organization’s normal verification process.
Once inside, the attacker may move toward less monitored areas. They could photograph documents, connect a device to an exposed computer, access an unlocked workstation, steal equipment, or gather information for a future attack. Even a short period of unauthorized physical access can create serious security and privacy risks.
Tailgating vs Piggybacking in Cyber Security
Tailgating and piggybacking are often used interchangeably, but some security professionals make a distinction between them. Tailgating generally describes an attacker entering behind an authorized person without that person’s explicit knowledge. The attacker may simply catch the door before it closes or blend into a group entering the building.
Piggybacking usually refers to situations where the authorized person knowingly allows another individual to enter with them. For example, an employee may hold the door for someone who says they forgot their access card. The employee may believe they are helping a legitimate coworker without realizing that they are bypassing security controls.
Both behaviors create similar risks because unauthorized access occurs without proper authentication. From a practical security perspective, organizations should discourage employees from allowing unverified individuals through restricted entrances. Every person should authenticate independently unless an approved visitor or escort procedure specifically allows another method.
Why Is Tailgating Considered Social Engineering?
Social engineering attacks exploit human behavior instead of relying entirely on technical weaknesses. Tailgating works because people are often uncomfortable closing doors in someone’s face or asking strangers to prove who they are. Attackers use this natural politeness to bypass physical access controls that would otherwise block them.
Confidence can also make the attack more convincing. Someone who walks quickly, wears appropriate clothing, or acts familiar with the building may appear legitimate even when nobody recognizes them. Employees may assume the person belongs there because challenging them can feel awkward or unnecessarily confrontational.
The same manipulation principles appear in digital attacks. For example, phishing in cyber security uses trust, urgency, and impersonation to persuade victims to take risky actions online. Tailgating applies similar psychological tactics in a physical environment rather than through emails or fake websites.
Common Examples of Tailgating Attacks
One common example involves an attacker carrying several boxes toward a secured office entrance. An employee sees that their hands are full and holds the door open as a courtesy. The attacker enters without presenting an access badge, creating an opportunity to reach internal areas that should require authorization.
Another example occurs during busy morning arrival periods. Several employees scan their badges and walk through the entrance together, while an unauthorized person blends into the group. Because the area is crowded, nobody notices that one person entered without authenticating through the access control system.
Attackers may also impersonate contractors or maintenance workers. A person wearing a uniform and carrying tools can appear trustworthy enough that employees assume someone else has already verified them. If visitor procedures are weak, the attacker may gain access to server rooms, offices, or network equipment simply by appearing professional.
Why Tailgating Is Dangerous for Businesses
Physical access can give attackers opportunities that would be difficult to achieve remotely. Once inside a building, an intruder may encounter unlocked computers, printed documents, employee badges, network ports, removable storage devices, or confidential conversations. These physical resources can support later cyberattacks even if the attacker does not immediately steal anything.
An attacker could also install malicious hardware. For example, they might connect an unauthorized device to a network port or leave a compromised USB drive where an employee could find it. Physical access makes it easier to bypass some remote security controls because the attacker is operating from inside the organization’s environment.
The financial and reputational consequences can also be significant. Unauthorized entry may contribute to data breaches, theft, business disruption, regulatory problems, or loss of customer trust. Organizations that protect sensitive information should therefore treat physical security as an essential part of their overall cyber security program.
Warning Signs of a Tailgating Attempt
Someone repeatedly waiting near a secured entrance may deserve closer attention. They may appear to be checking their phone while watching how employees enter or waiting for a convenient person to open the door. This behavior does not automatically indicate malicious intent, but it can justify normal identity verification.
Another warning sign is a person claiming they forgot or lost their access badge. Legitimate employees should normally follow an established process for replacement or temporary access. A stranger who pressures someone to ignore that process because they are late or in a hurry may be attempting to bypass security.
Unfamiliar people wandering in restricted areas without a visible visitor badge or escort should also be reported. Employees do not need to confront suspicious individuals aggressively. Following company procedures, contacting security, or politely directing the person to reception can resolve legitimate situations while reducing the risk of unauthorized access.
How to Prevent Tailgating Attacks
The simplest prevention measure is requiring every person to authenticate individually before entering a controlled area. Employees should avoid holding secured doors open for unknown individuals, even when doing so feels polite. Legitimate visitors and employees without badges should use official reception, visitor management, or temporary-access procedures instead.
Physical controls can strengthen this policy. Turnstiles, security guards, badge-controlled doors, cameras, mantraps, and anti-tailgating sensors can make unauthorized entry more difficult. The appropriate controls depend on the sensitivity of the location, because a public office lobby may require different protection from a data center or research facility.
Training is equally important because technology cannot prevent every social engineering situation. Employees should understand why tailgating is risky and how to respond without creating unnecessary conflict. Clear instructions make it easier to challenge unusual access appropriately rather than expecting workers to make security decisions without guidance.
Role of Access Control in Preventing Tailgating
Access control systems determine who can enter specific locations and when that access is permitted. Key cards, badges, PINs, mobile credentials, and biometric systems can all help verify identity before a door unlocks. However, their effectiveness depends on each individual actually using the system rather than entering behind someone else.
Organizations should also follow the principle of least privilege for physical access. Employees should only be able to enter areas needed for their responsibilities. Limiting access reduces the impact of stolen credentials and makes it easier to identify unusual behavior when someone appears in an area where they do not normally belong.
Access records can support investigations as well. Logs can show which badge opened a door and when, while cameras may provide additional context. Combining electronic access controls with monitoring helps security teams identify patterns such as repeated door entries that do not match the number of people physically entering.
How Employee Training Reduces Tailgating Risk
Security awareness programs should explain tailgating using realistic examples rather than simply telling employees not to hold doors. People need to understand how attackers create believable situations and why bypassing authentication matters. When employees see the connection between physical entry and cyber threats, security policies become easier to take seriously.
Training should also provide simple scripts or actions employees can use. A worker might politely say that company policy requires everyone to use their own badge or direct visitors to reception. Knowing what to do in advance reduces hesitation when an unfamiliar person attempts to follow them through a secured entrance.
Regular reminders can reinforce good habits because employees may become less cautious over time. New staff, contractors, and temporary workers should receive the same guidance. Security culture becomes stronger when protecting restricted areas is treated as a normal workplace responsibility rather than something handled only by guards or IT teams.
What Should You Do If Someone Tailgates You?
If you notice someone entering behind you without authenticating, follow your organization’s security procedure. That may involve politely asking whether they have a badge, directing them to reception, or contacting security staff. Avoid putting yourself in danger by physically confronting someone who appears aggressive or threatening.
If the person has already entered a restricted area, report where you last saw them and provide a description if requested. Quick reporting can allow security teams to verify whether the person is an authorized visitor. Waiting until later may give an intruder more time to move around the building unnoticed.
Employees should also report recurring access-control problems. A door that closes too slowly, a broken badge reader, or an entrance that is regularly left unsecured can make tailgating easier. Fixing these weaknesses can prevent future incidents rather than relying entirely on employees to notice suspicious behavior every time.
Tailgating and Physical Security Best Practices
Organizations should clearly separate public areas from employee-only and highly restricted zones. Reception areas, visitor badges, escorts, and controlled internal doors help prevent someone who legitimately enters the lobby from freely reaching sensitive locations. Layered physical security reduces the damage one failed control can cause.
Doors protecting sensitive areas should close and lock automatically rather than depending on employees to secure them manually. Access systems should also be tested regularly to identify damaged locks, sensors, or readers. Poorly maintained physical controls can turn a strong written policy into something that provides little practical protection.
Visitor management should be equally structured. Visitors should be registered, identified, given appropriate temporary credentials, and escorted where necessary. When legitimate visitors are easy to recognize, employees are more likely to notice someone who is moving through the building without proper identification.
Tailgating in Remote and Hybrid Work Environments
Hybrid work does not eliminate tailgating risks. Offices may actually become harder to monitor when fewer employees are present and coworkers no longer recognize everyone who regularly uses the building. Shared coworking spaces can add another challenge because multiple organizations may use the same entrances and common areas.
Companies should review physical security whenever workplace arrangements change. Badge access, visitor procedures, reception staffing, and restricted zones may need adjustment if offices operate differently than they did previously. Employees who visit only occasionally should still receive clear reminders about entry procedures.
Remote workers can also contribute to physical security by protecting access credentials. Employees should report lost badges quickly and avoid lending cards to colleagues. A stolen or shared badge can make unauthorized entry easier and may reduce the effectiveness of logs used to identify who entered a location.
Tailgating Prevention Checklist for Organizations
Start by identifying which areas require controlled access and how sensitive each location is. Server rooms, records storage, laboratories, executive offices, and network closets may require stronger controls than general workspaces. Matching protection to actual risk helps organizations invest resources where physical intrusion would create the greatest damage.
Next, review the complete access process from arrival to departure. Check whether visitors are registered, employees use individual badges, doors close properly, and lost credentials are disabled quickly. Security teams should also determine whether cameras, guards, or electronic logs provide enough visibility into unusual access events.
Finally, reinforce procedures through awareness training and periodic testing. Employees should know how to report suspicious behavior, where visitors should go, and why sharing access is prohibited. Effective tailgating prevention combines technology, physical design, policy, and human awareness instead of depending on any single control.
Conclusion
Tailgating in cyber security is a social engineering technique that allows unauthorized individuals to enter restricted physical areas by following authorized people. The attack often succeeds because employees want to be helpful or assume an unfamiliar person belongs there. Even simple acts such as holding a secure door open can unintentionally bypass important access controls.
Preventing tailgating requires more than installing badge readers. Organizations need clear entry procedures, visitor management, employee training, properly maintained doors, appropriate monitoring, and stronger controls around high-risk areas. Employees should also feel comfortable following security policy even when doing so means asking someone to authenticate separately.
Physical security and cyber security are closely connected. An intruder who reaches internal workspaces may gain access to devices, documents, network connections, or sensitive information that supports a larger cyberattack. Building a culture where every person verifies access properly can significantly reduce this overlooked but important security risk.
FAQs
What is tailgating in cyber security in simple words?
Tailgating is when an unauthorized person enters a restricted area by following someone who has legitimate access. The attacker avoids using their own badge, key, or other required authentication method.
Is tailgating a social engineering attack?
Yes. Tailgating is social engineering because attackers exploit human behavior such as politeness, trust, distraction, or fear of confrontation rather than relying only on technical vulnerabilities.
What is an example of tailgating?
An attacker may carry boxes toward a secured office door and wait for an employee to hold it open. The attacker then enters without using an authorized access badge.
How can companies prevent tailgating?
Companies can use individual badge authentication, turnstiles, security guards, visitor procedures, employee awareness training, cameras, and properly secured doors. Sensitive areas may require additional access controls and monitoring.
What is the difference between tailgating and piggybacking?
Tailgating often refers to unauthorized entry without the authorized person’s awareness, while piggybacking may involve someone knowingly allowing another person through. Both can bypass physical security controls.




